Threat intelligence analysts and builders. Talk to someone who does this work, and get a straight answer.
Contact usGet a DemoStart a free trial
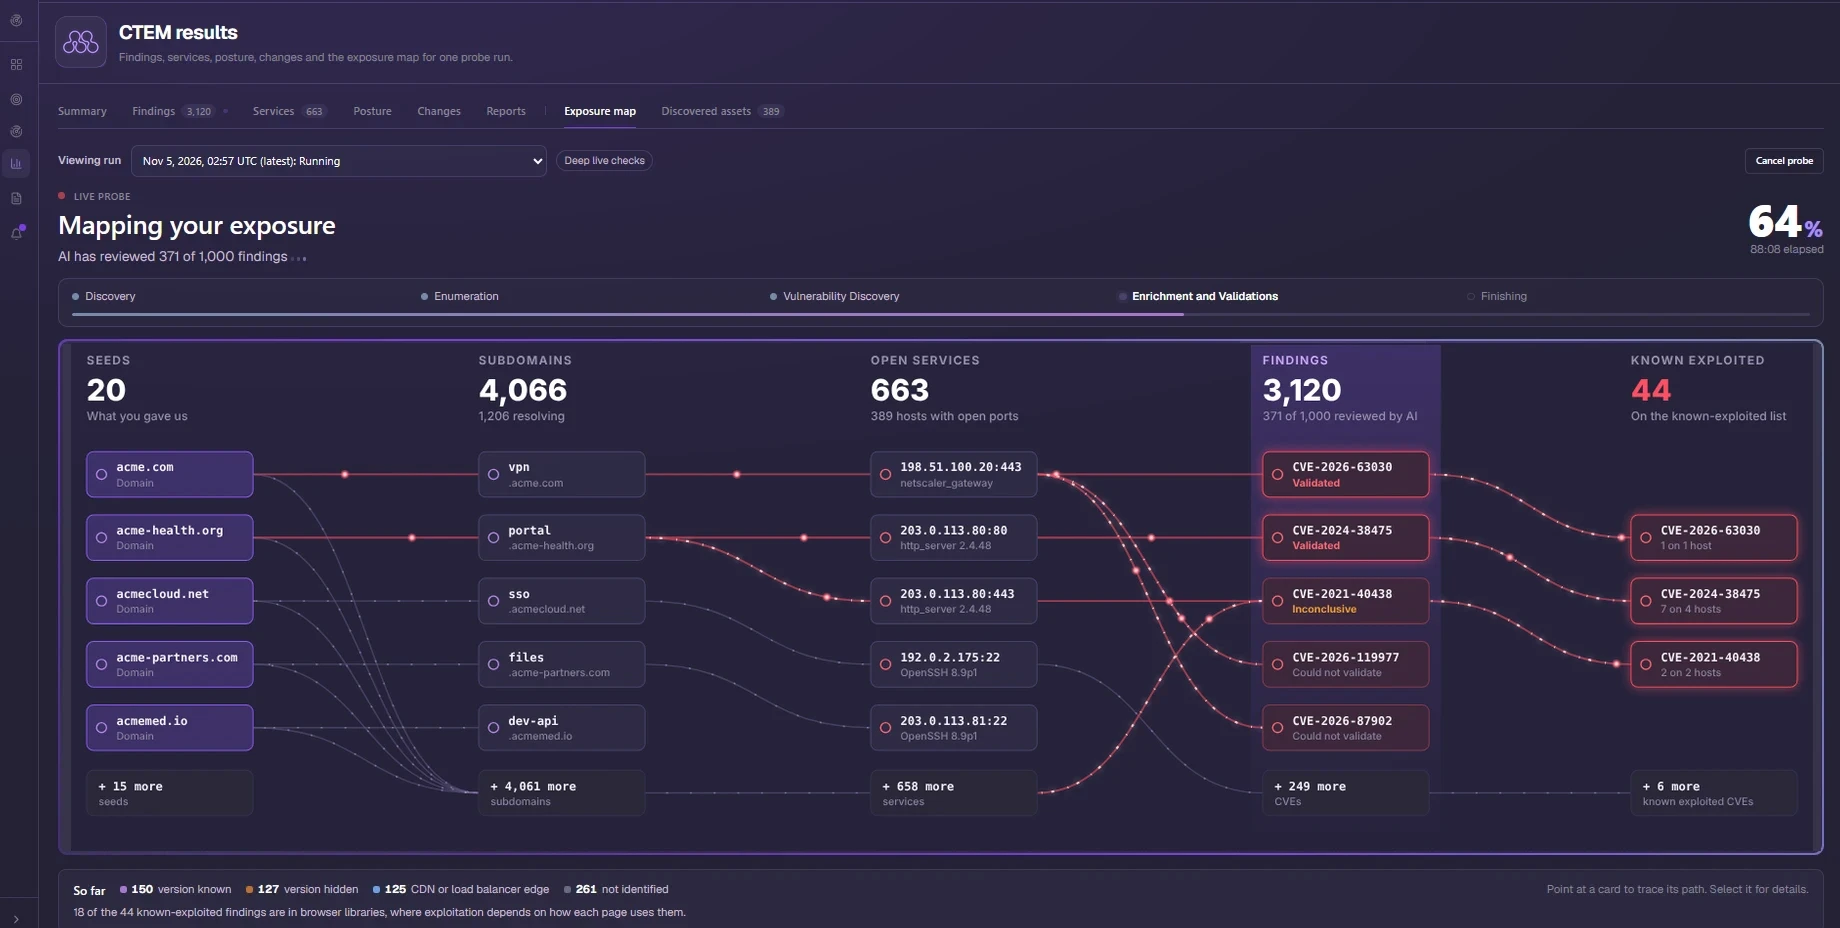
From the domains you give us to the vulnerabilities attackers use.
Morado starts from your seed domains, discovers subdomains and open services, finds vulnerabilities, validates what it can live, and traces each path to the known-exploited list. The red paths are the ones that need action now.
- Discovery
- Enumeration
- Vulnerability discovery
- Enrichment and validation
- Finishing
Example data. Domains and IP addresses are fictional.
What Exposure Management covers.
Live Exploitability Validation
For supported vulnerabilities, Morado's proprietary technology tests the affected in-scope system live, to show whether a discovered vulnerability is actually exploitable in your environment.
- Particular focus on internet-facing edge devices, where weaknesses give attackers initial access
- Validation evidence stays connected to the asset and vulnerability
- A confirmed exploitable finding is a strong basis for escalation
- An unsuccessful or inconclusive test is read within its scope, not mistaken for a fix
Scope & Discovery
Start from the domains, IP addresses and CIDR ranges you need assessed, or import them from your cloud accounts, then scan for exposures, misconfigurations, expiring certificates and vulnerabilities.
- Connect cloud accounts with read-only credentials, including AWS, Azure, Google Cloud and other major providers, to suggest public IPs, hostnames and DNS zones
- Nothing becomes a monitored asset until you accept it, and Morado never changes anything in your cloud account
- Exposed services, misconfigurations, certificate issues and vulnerabilities in one assessment
- Repeated assessments build a history of your attack surface
Drift & Change Tracking
Morado compares each assessment with the last, so you see how exposure is changing: what is new, what persists, what disappeared and what came back.
- Newly discovered assets, services and vulnerabilities
- Changes in software, configuration and certificates
- Findings that disappear after remediation, and resolved exposures that return
- Assessment context kept, so a host that couldn't be scanned isn't mistaken for a fix
Threat Context & Prioritization
Morado vulnerability intelligence shows which threats are relevant to your exposed systems and why particular findings deserve attention.
- External accessibility, threat relevance, validated exploitability and drift together
- Exploited vulnerabilities and the actors using them, connected with Intel Operations
- A clear answer to what should be fixed first, and the evidence behind it
Internal Scanner Data
Integrations with popular internal vulnerability scanners, such as Qualys, bring their findings into the same process, enriched with Morado vulnerability intelligence.
- Internal and external findings evaluated together
- Source retained on every imported finding
- Relevant intelligence shared with the teams that fix
Notify, Rescan & Verify
Deliver findings to the people who make the fix, with the context they need, then rescan to confirm the outcome.
- Notifications to vulnerability management, infrastructure, cloud, application, security operations and business owners
- Asset, weakness, threat activity, potential impact, validation evidence and drift in one message
- Rapid rescanning, and repeat validation for supported vulnerabilities
- Later scans watch for recurrence, connecting discovery, evidence, verification and any regression
See Exposure Management at work.
 Click to enlarge
Exposure Management in practice.
A relevant news story
- News Stream brings related reporting into one story and extracts IOCs, vulnerabilities, TTPs, threat actors and third parties.
- An analyst uses Morado AI and connected platform capabilities to assess relevance to the organization.
- Findings lead to hunts, coverage assessments, exposure checks and recommendations.
A third-party breach
- Third-party monitoring identifies an incident.
- A workflow investigates the actor, hunts for indicators, checks TTP coverage and examines relevant vulnerabilities.
- Relevant findings are escalated to the teams responsible for action.
Built to run a CTEM program.
CTEM is a continuous cycle, not a one-time scan. Morado supports each of its five stages in one platform, and drift monitoring connects each cycle to the next: is exposure growing, did the fixes work, and are they holding?
Know what is exposed, what changed, what is exploitable, and whether the fix worked.
Software and analyst expertise, together.
See Morado in action.
Book a demo and see Morado built around your organization: your exposure, your threats and the workflows to act on them.
Questions first? Contact us.