Threat intelligence analysts and builders. Talk to someone who does this work, and get a straight answer.
Contact usGet a DemoStart a free trial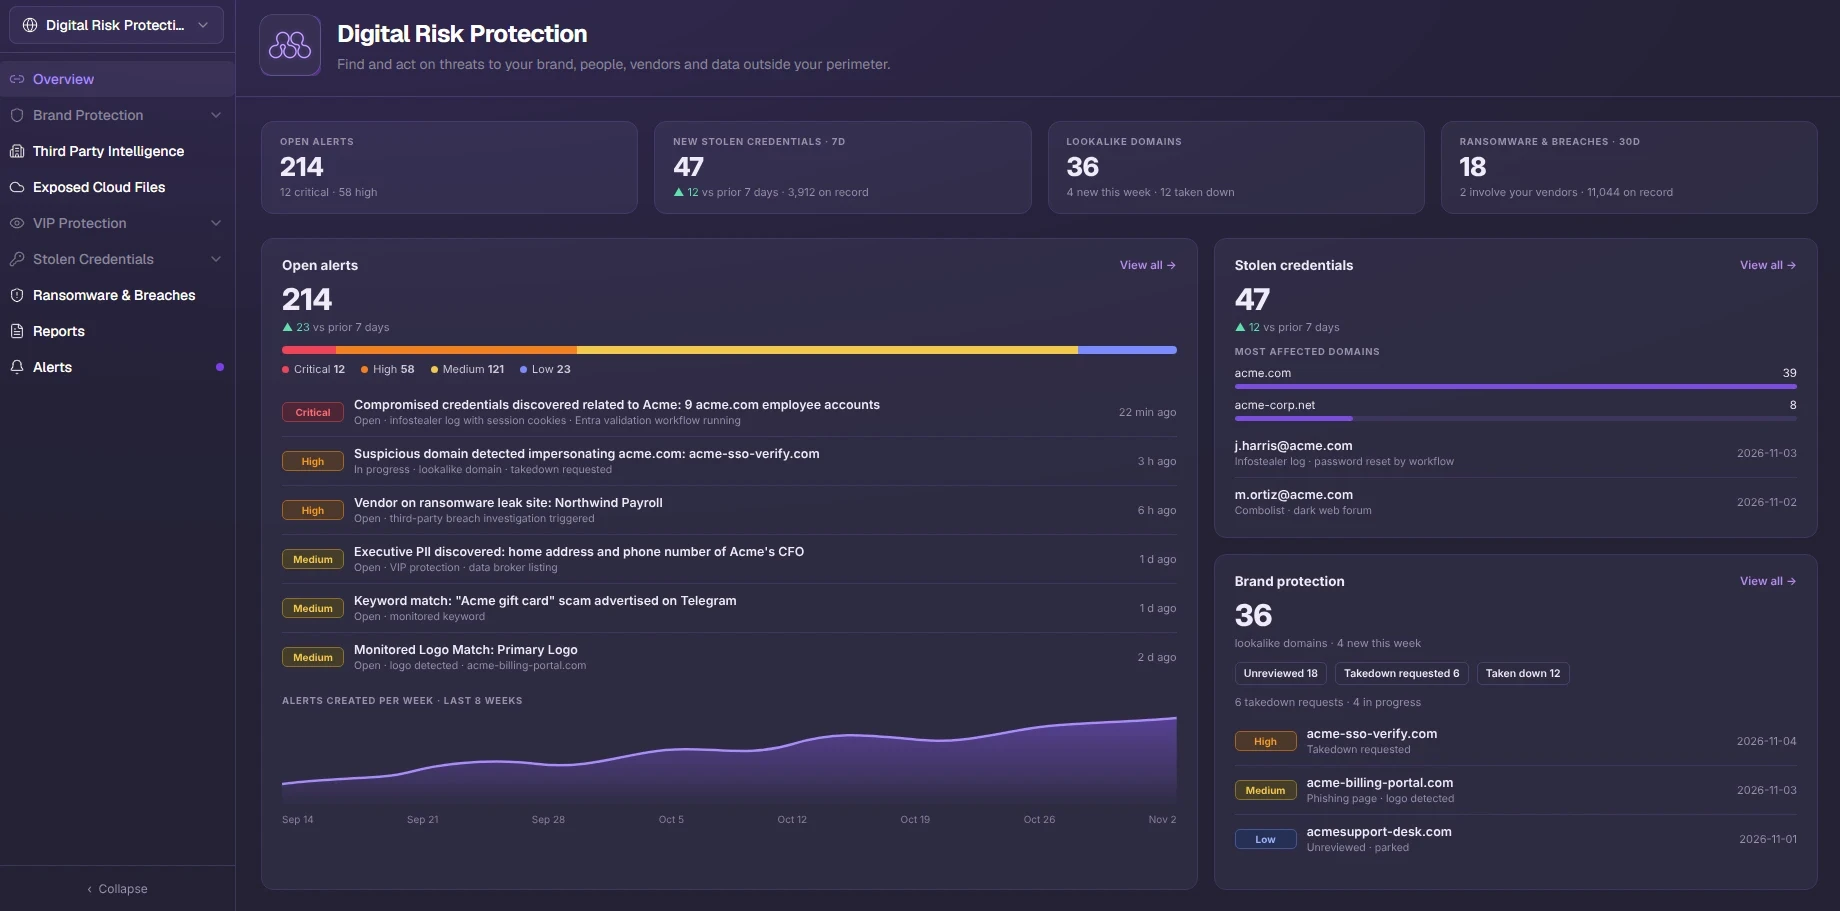
What Digital Risk Protection covers.
Compromised Credentials
Credentials tied to employees and relevant partner identities, from breach data, credential collections and stealer logs offered to attackers, assessed for whether they are a usable path in.
- Source, age, affected service and credential material considered for each finding
- Password-policy filtering helps prioritize what may still be live
- Validation workflows with Microsoft Entra, using the checks your integration and permissions allow
- Case workflows to request relevant credential material from dark web marketplaces as evidence
- Each finding ends in a decision: investigate, remediate, escalate or close
Your Digital Footprint
Monitoring is organized around what needs protection: your brands, domains, applications, executives, employee identities, relevant partner accounts and third-party relationships.
- Protected entities separate relevant findings from unrelated references
- One discovery can affect several areas, such as a domain that targets an executive, collects credentials and imitates a supplier
- Related findings are connected so teams investigate the broader activity together
Brand Protection
Find domains, mobile apps and social media profiles that impersonate your organization or misuse its brand, from phishing and fake support to counterfeit apps and payment diversion.
- Lookalike domains and sites posing as your services, with screenshots, WHOIS and change history
- Impersonating mobile apps and social media accounts
- Similarity is a starting point; content, behavior and audience decide what is a real threat
- Preserve evidence, group related findings into a case, and request takedowns
Stealer-Log Intelligence
Stealer logs for sale can expose logins and session material from infected employee, partner or customer devices. Morado connects them to affected identities and services.
- Hosts in a listing matched against your monitored assets
- Points to device-level compromise that needs more than a password reset
- Related records grouped to show one device, repeated exposure or a wider pattern
Executive & VIP Protection
Monitor exposed information and impersonation involving executives and other designated people, which can make fraud and social engineering far more convincing.
- Exposed personal details and credentials rated by risk
- Fake executive profiles that approach employees, partners or customers
- Access to sensitive findings limited to the people handling them
Third-Party Intelligence
Ongoing intelligence on the suppliers, service providers and partners whose security affects you, between scheduled assessments.
- Reported breaches, spikes in exposed data and visible weaknesses
- Risk scores, chatter and risk events for each vendor on your watchlist
- Does this provider hold our data? Could an incident affect a critical service?
- Findings routed to security, procurement, vendor management, legal or the business owner
Exposed Cloud Files
Publicly accessible files, code and paste content associated with your organization, so you can see what outsiders can discover.
- Internal documents, operational details, employee or customer information
- Decide whether an exposure is authorized, needs restricted access, or should be removed
- Related findings connected when they point to a broader sharing or configuration issue
Ransomware & Breach Intelligence
An extensive collection of ransomware and breach claims, by threat group, industry and region, to find claims about you, your third parties and anyone relevant to your risk.
- Claims that name you directly, and your files appearing in a supplier's or partner's breach
- Dark web mentions, sources and links in the intelligence graph for each breach
- A claim is a lead: investigators record what is confirmed, what is uncertain, and who needs to respond
Cases & Remediation
Triage findings, assign owners, collect evidence, coordinate action and track progress, with related discoveries combined into one case.
- Credential, impersonation, exposed-file, executive and third-party cases
- Takedown support from Morado within the agreed service scope
- Closure records the disposition and evidence: remediated, authorized, false positive or otherwise resolved
- Follow-up monitoring catches recurring exposure
Prioritization & Reporting
Prioritize by organizational impact, and give each team what it needs to act.
- Affected identity or asset, freshness and credibility of evidence, sensitivity and potential access
- Evidence for security operations, credential cases for identity teams, impersonation for brand teams, vendor assessments for owners
- Leadership views of material exposure, active cases and remediation progress
Digital Risk Protection in practice.
A compromised credential
- Digital Risk Protection identifies an exposed credential.
- A workflow checks the account through the Microsoft Entra integration and performs the configured validation and protection actions.
- The user is notified.
A third-party breach
- Third-party monitoring identifies an incident.
- A workflow investigates the actor, hunts for indicators, checks TTP coverage and examines relevant vulnerabilities.
- Relevant findings are escalated to the teams responsible for action.
An executive trip
- Intel Operations captures stakeholder questions.
- Digital Risk Protection contributes relevant exposure. Physical Security contributes destination reporting and geographic context.
- Analysts deliver an assessment. Stakeholders review it, give feedback and open RFIs.
Know what is exposed outside your perimeter, decide what matters, and document how it was resolved.
Software and analyst expertise, together.
See Morado in action.
Book a demo and see Morado built around your organization: your exposure, your threats and the workflows to act on them.
Questions first? Contact us.